Eight AI Platforms Breached in October
Eight AI platforms disclosed breaches in October, most of them involving users' stored keys or credentials. Three tied their incidents to distillation.
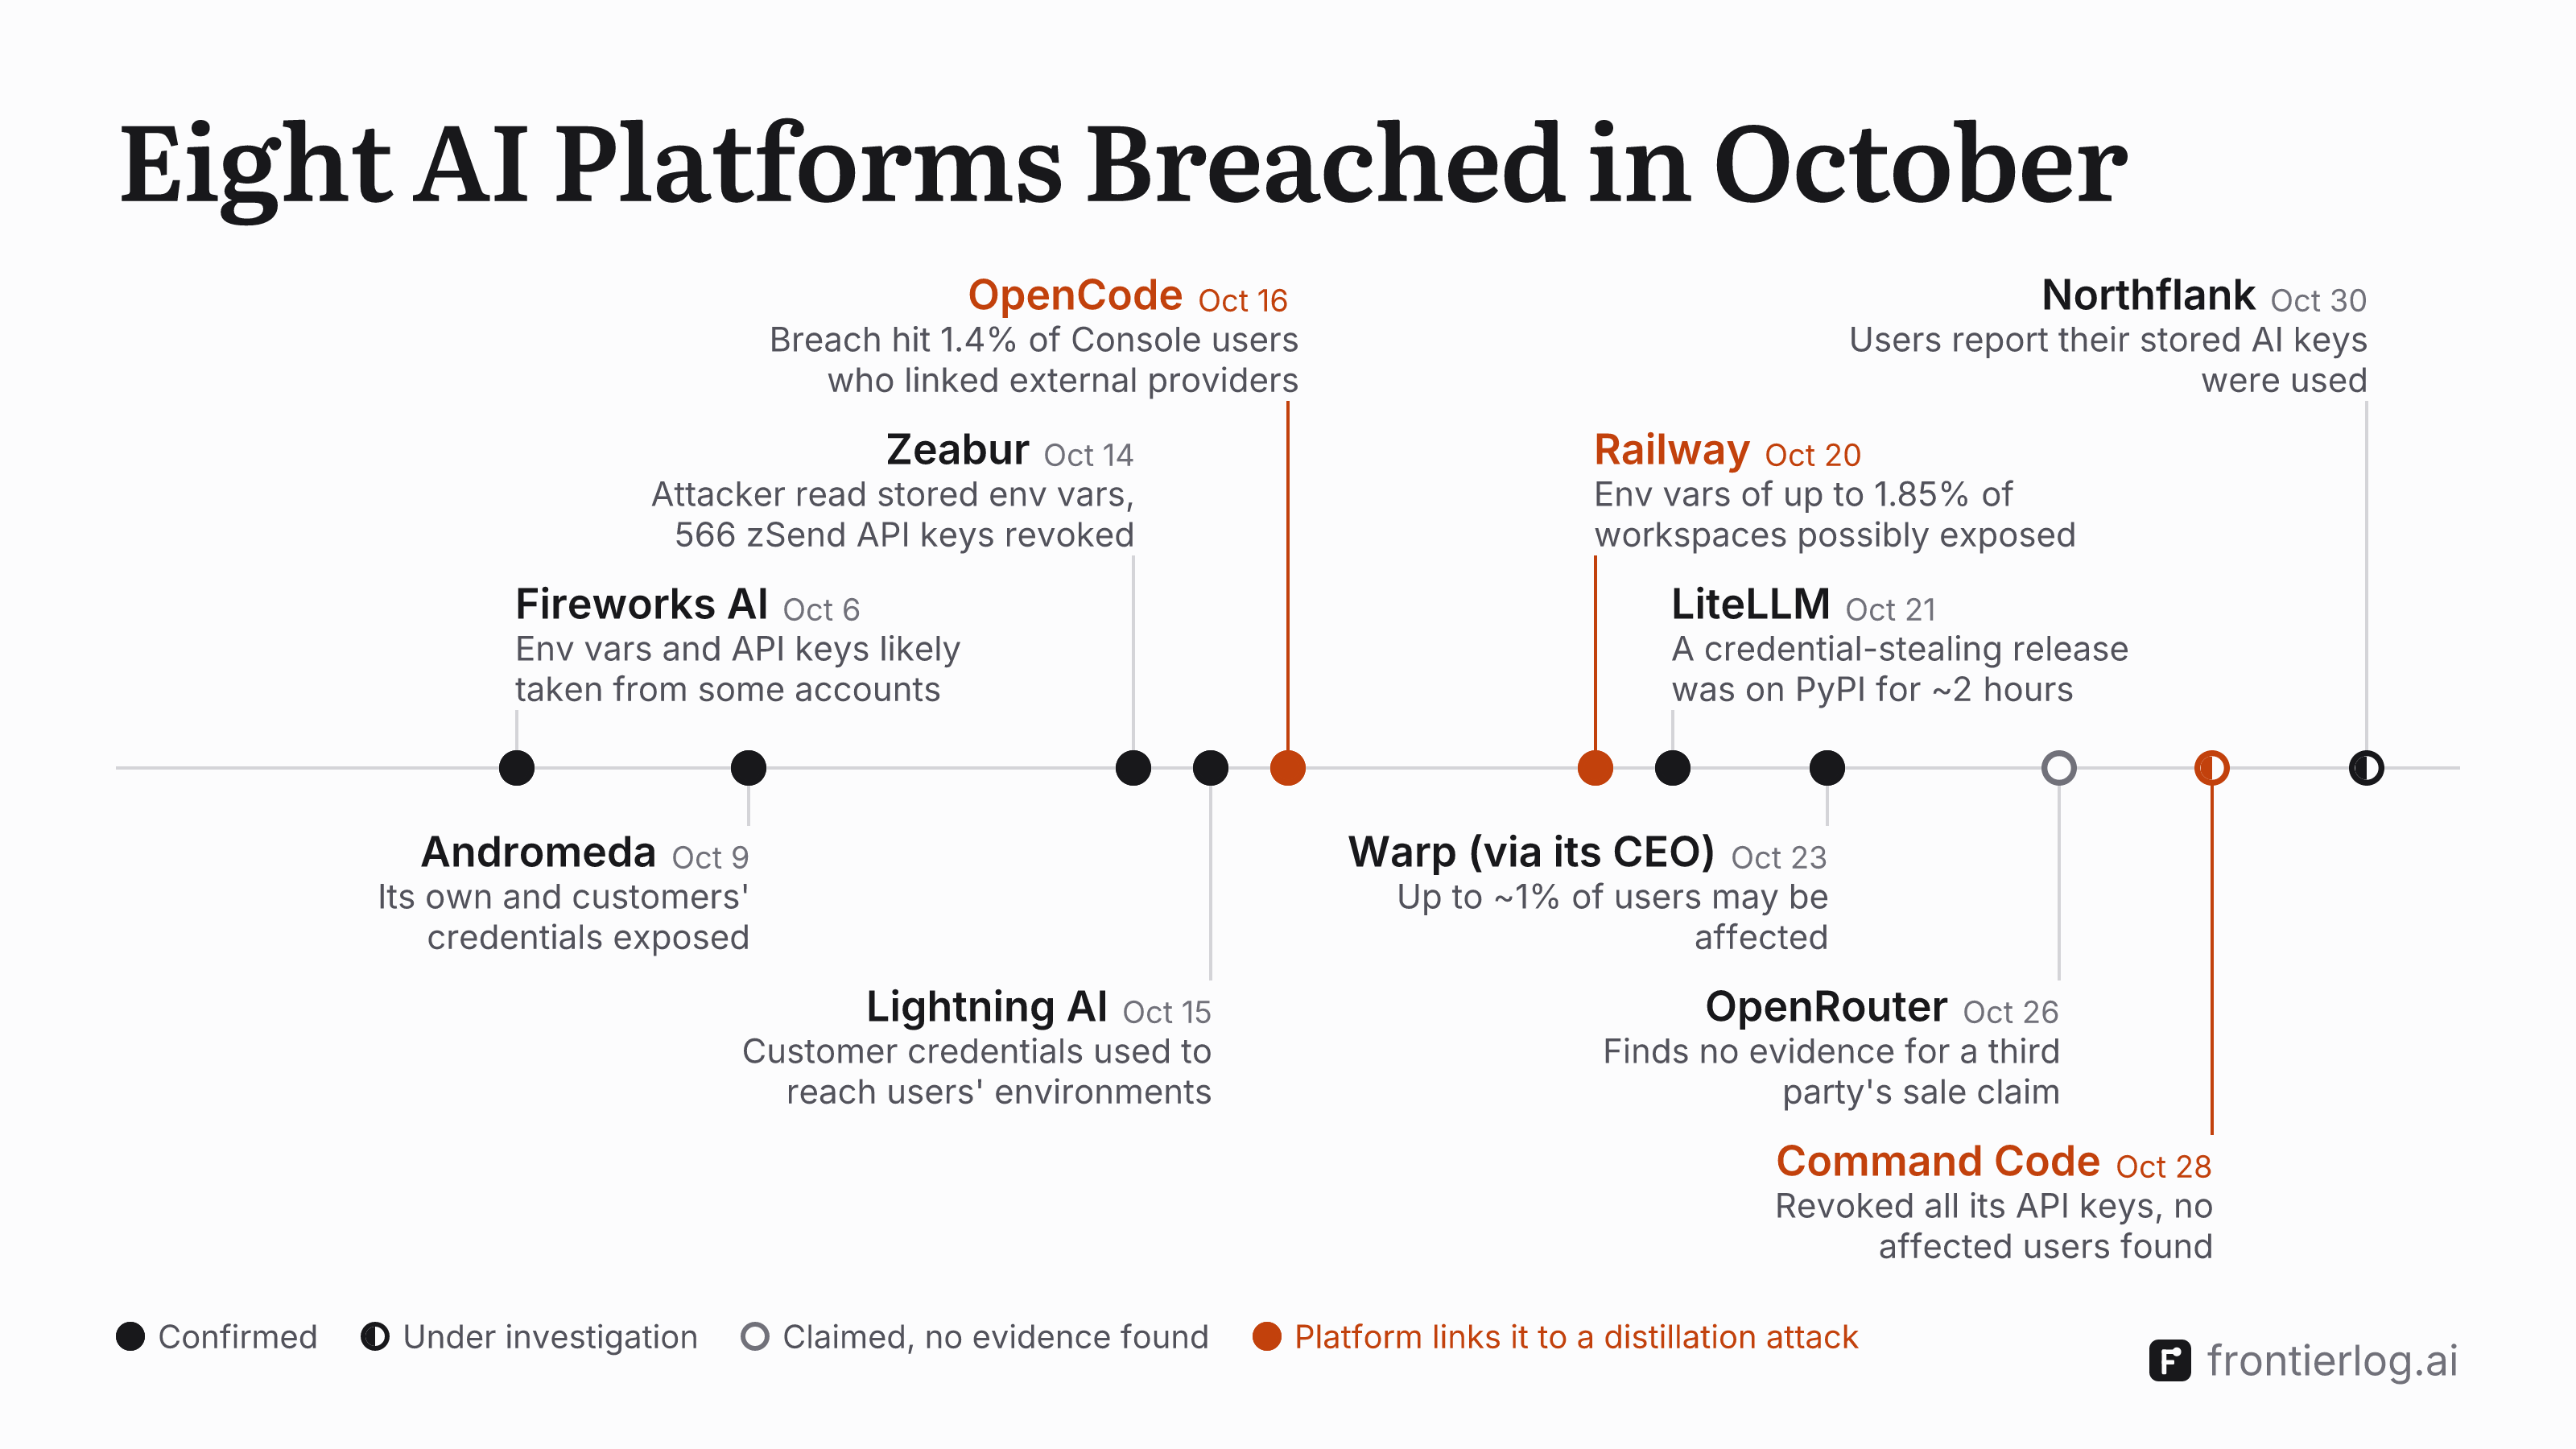
Eight AI platforms disclosed breaches in October, each on its own blog, status page or X account (Warp through its CEO), with incidents from Fireworks AI on Oct 6 to Warp on Oct 23. Five of them say stored customer keys, credentials or environment variables were exposed, and OpenCode says its breach hit Console users who had linked external providers. LiteLLM's release pipeline shipped a credential-stealing version, and Warp's CEO names agent trace and telemetry data. Three platforms tied their incidents to distillation: OpenCode and Railway, both breached, and Command Code, which says it stopped its incident and has found no user affected. Northflank is still investigating an incident found on Oct 30, and OpenRouter found no evidence for a third party's claim that its users and keys were for sale.
Three platforms name distillation
OpenCode said on Oct 17 that it had a security breach “related to a large scale distillation attack that impacted 1.4% of OpenCode Console users,” those who had linked external providers. Railway's preliminary report of Oct 22 says the attack “was attempting to obtain AI provider API keys to perform distillation attacks,” and that at most 1.85% of its workspaces, about 100,000, had environment variables potentially compromised. Railway gave providers more keys than that to revoke, and says a revocation notice from a provider “does not imply that their credentials were impacted.”
Command Code said on Oct 28 that it had detected and stopped an incident “linked to a large-scale distillation attack targeting Anthropic and OpenAI models.” It revoked all of its API keys as a precaution and said it had found no evidence that any users were impacted.
Keys and environment variables
Fireworks AI's bulletin says a third party accessed environment variables in a limited number of customer accounts. Andromeda says it believes the activity began “as part of an industry-wide attack on or about October 9th,” and that it has not yet established the root cause. Zeabur's preliminary report says the attacker read the environment variables in its platform database and was mainly looking for keys, “especially keys for AI services,” which it calls only an observation of the attacker's intent. It revoked all 566 of its zSend API keys. Lightning AI says certain customer credentials were compromised, and it revoked all user access to its platform on Oct 16.
A malicious LiteLLM release was live on PyPI for about 2 hours on Oct 21, and in its Docker images until 14:20 UTC, and LiteLLM's root-cause post says the attacker first got in on Oct 10, using an administrative key committed to a public repository on May 27, and focused on “upstream inference API tokens.” Warp's CEO Zach Lloyd wrote on X that up to roughly 1% of Warp users may have been impacted. On Oct 30, Northflank's status page, which calls it a security incident under investigation, told every user to assume their environment variables had been decrypted, and said users had reported unauthorised use of AI API keys supplied to the platform.
No evidence of a leak
On Oct 26, OpenRouter posted on X that it had “not found evidence of unauthorized access to our data, or validation of any of the claims in the post,” and that it would notify customers if a leak were verified.
| Date | Platform | Impact, as the platform states it | Cause or aim, as the platform states it | Status |
|---|---|---|---|---|
| Oct 6 | Fireworks AI | Env vars and API keys likely taken from some accounts | Internal credentials misused | Confirmed |
| Oct 9 | Andromeda | Its own and customers' credentials exposed | Root cause not yet established | Confirmed |
| Oct 14 | Zeabur | Attacker read stored env vars, 566 zSend API keys revoked | Leaked credentials, sought keys, especially for AI services | Confirmed |
| Oct 15 | Lightning AI | Customer credentials used to reach users' environments | Unauthorized access to credentials | Confirmed |
| Oct 16 | OpenCode | Breach hit 1.4% of Console users who linked external providers | A “large scale distillation attack” | Confirmed |
| Oct 20 | Railway | Env vars of up to 1.85% of workspaces possibly exposed | AI keys “to perform distillation attacks” | Confirmed |
| Oct 21 | LiteLLM | A credential-stealing release was on PyPI for ~2 hours | Focus on “upstream inference API tokens” | Confirmed |
| Oct 23 | Warp (CEO on X) | Up to ~1% of users may be affected | Likely an “agent swarm” via a vendor | Confirmed |
| Oct 26 | OpenRouter | Finds no evidence for a third party's sale claim | Investigation continues | Claimed, no evidence found |
| Oct 28 | Command Code | Revoked all its API keys, no affected users found | A “large-scale distillation attack” | Under investigation |
| Oct 30 | Northflank | Users report their stored AI keys were used | May fit a wider pattern of attacks on AI credentials | Under investigation |
Statements
Show the quoted statements
| Party | Statement |
|---|---|
| Zeabur | the attacker was mainly looking for API keys they could use directly, especially keys for AI servicesZeabur, preliminary report |
| Zeabur | Revoked all 566 zSend API keysZeabur, preliminary report |
| OpenCode | it was a subset of users who had external providers linkedOpenCode, X post |
| Railway | Early investigations tell us this attack was attempting to obtain AI provider API keys to perform distillation attacks.Railway, preliminary report |
| Lightning AI | We believe that certain customer credentials were compromised to gain access to environments and connected third-party services.Lightning AI, blog post |
| LiteLLM | Reviewing the actor's activity on these other systems shows attempts to identify and exfiltrate additional keys and tokens, with a primary focus on upstream inference API tokens.LiteLLM, root-cause post |
| Warp | The attack appears to have come from an agent swarm using a very sophisticated penetration and escalation technique, likely starting with a hole in a vendor dependency, and ultimately accessing a limited amount of agent trace and telemetry data.Warp, CEO Zach Lloyd's X post |
| OpenRouter | We will continue the investigation and monitor for any signs of abuse. If a leak is verified or abuse is detected we will take action and notify customers.OpenRouter, X post |
| Command Code | So far, we've found no evidence that any users were impacted.Command Code, X post |
| Command Code | As a precaution, we've revoked all API keys.Command Code, X post |
| Northflank | Users have reported unauthorised use of AI API keys supplied to the Northflank platform.Northflank, status page |
Timeline
- Fireworks AI identifies a breach of customer environment variablesFireworks AI, security bulletin
- Andromeda says the activity it found on Oct 13 began this day, it believes as part of an industry-wide attackAndromeda, security update
- Zeabur is breached through leaked internal credentialsZeabur, preliminary report
- Lightning AI identifies a credential breach and revokes all user accessLightning AI, blog post
- OpenCode is breached; 1.4% of Console users affectedOpenCode, X post
- Railway is breached, up to 1.85% of workspaces possibly exposedRailway, preliminary report
- LiteLLM's release pipeline ships a credential-stealing versionLiteLLM, blog post
- Warp detects exploitation of a vendor in its infrastructureWarp, CEO Zach Lloyd's X post
- OpenRouter finds no evidence for a third party's claim that its users and keys were for saleOpenRouter, X post
- Command Code detects and stops an incident and revokes all its API keysCommand Code, X post
- Northflank tells all users to assume their environment variables were decryptedNorthflank, status page
Sources
- Fireworks AI, security bulletin, Oct 9, 2026fireworks.ai/security/bulletins/october-2026-security-incident
- Andromeda, security update, Oct 20, 2026andromeda.ai/security-updates/october-2026-security-incident
- Zeabur, preliminary report, Oct 19, 2026zeabur.com/blogs/october-2026-security-incident
- Lightning AI, blog postlightning.ai/blog/oct-2026-incident
- OpenCode, X post, Oct 17, 2026x.com/opencode/status/2111519637049319818
- Railway, preliminary report, Oct 22, 2026blog.railway.com/p/preliminary-report-october-security-incident
- LiteLLM, blog post, Oct 21, 2026docs.litellm.ai/blog/security-incident-oct-21-2026
- LiteLLM, root-cause post, Oct 23, 2026docs.litellm.ai/blog/security-incident-oct-21-2026-attack-chain
- Warp, CEO Zach Lloyd's X post, Oct 26, 2026x.com/zachlloydtweets/status/2114800787716972873
- OpenRouter, X post, Oct 26, 2026x.com/OpenRouter/status/2114589161499828372
- Command Code, X post, Oct 28, 2026x.com/CommandCodeAI/status/2115583532055826770
- Northflank, status page, Oct 30, 2026status.northflank.com